41Stack Overflow · architecture
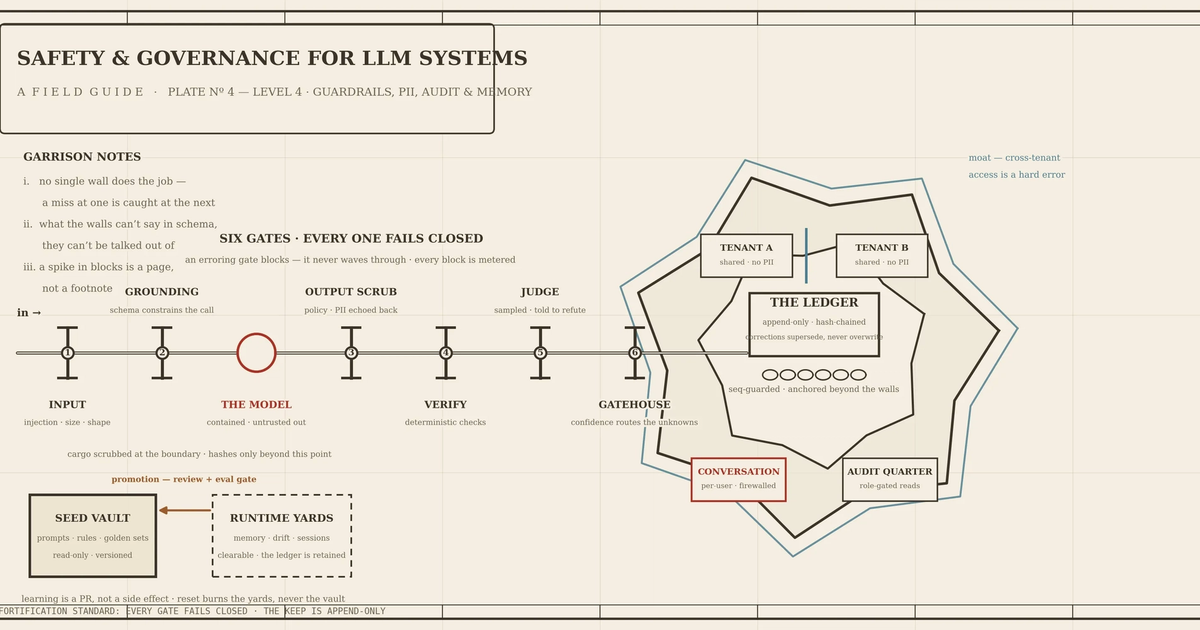
Part 4: Safety and governance for LLM systems: guardrails, PII, audit, and memory
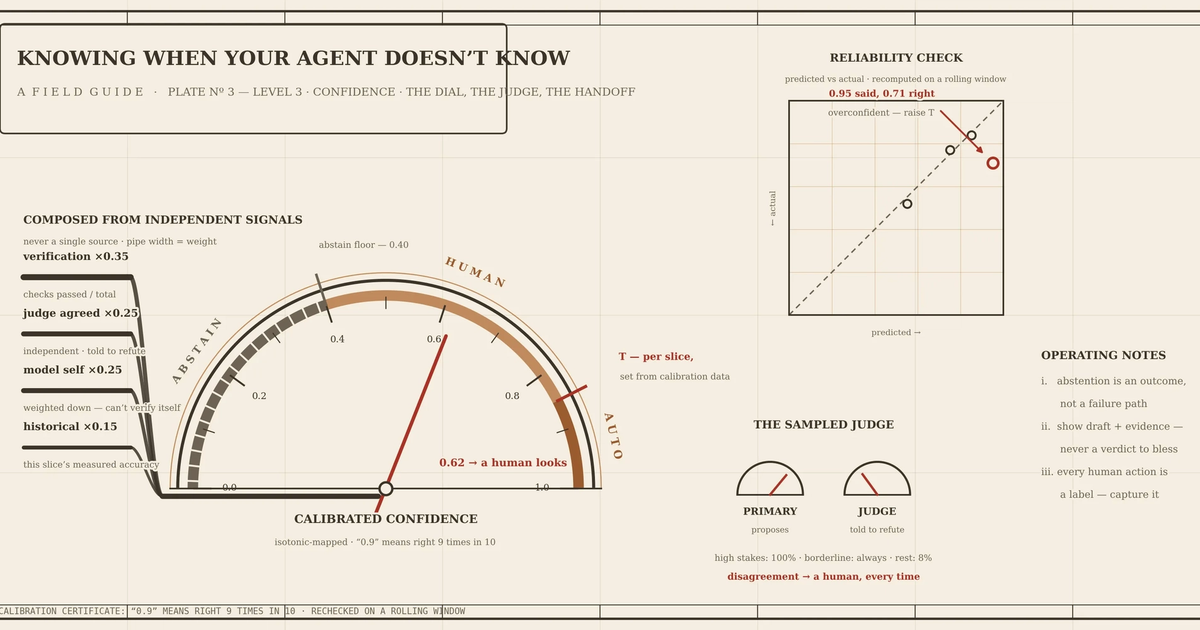
This post details safety and governance practices for LLM systems, focusing on layered guardrails, boundary-level PII handling, and immutable audit trails. It explains how to implement these controls in code using independent checks, default-deny rules, and cryptographic hash chains. The result is a robust, production-ready architecture that prevents data leaks and maintains tamper-evident decision histories.
DEPTH ■■■■■19 min read2 weeks ago