/ THE FEED /

Read what ships.

Deep, recent reads ranked by depth and freshness.

  1. Origin Range Requests: Serving large files without range-request tuning

    Cloudflare replaced a legacy, fixed-size range caching design that suffered from bandwidth waste and memory pressure with a Pingora-based chunk coordinator. The new implementation dynamically combines cached chunks and aligned origin fetches to serve range requests accurately without manual tuning. This approach cut p99 time to first byte in half for R2 storage and reduced tiered cache traffic by six percent.

    DEPTH ■■■■■8 min read3 days ago

    DatabasesPerformanceRedis

    Sign in to save and rate

  2. Shard design doesn't start from your tables

    Designing a sharded Postgres architecture requires grouping tables around shared query keys rather than starting from table structures alone. The post details how to configure shard groups, reference tables, SQL expressions in shard indexes, and global secondary indexes using Neki. This setup enables efficient single-shard queries and transactions while maintaining full Postgres semantics.

    DEPTH ■■■■■8 min read3 days ago
    PostgreSQL

    Sign in to save and rate

  3. PHP2Shell: GitLab helps find and remediate critical PHP flaws

    Critical remote code execution vulnerabilities known as PHP2Shell affect the PHP engine across multiple versions, requiring immediate runtime updates to fixed versions or patched distribution packages. The team utilized platform features like container scanning, code search, and automated agent workflows to locate PHP projects and remediate vulnerabilities. Operators must also check logs and environments for signs of compromise as framework updates and input validations cannot prevent these engine-level flaws.

    DEPTH ■■■■■10 min read4 days ago

    ArchitectureSecurity

    Sign in to save and rate

  4. App stability at scale with a layered defense

    To maintain app stability amidst rapid weekly releases and AI-generated code, Grab uses a layered defense strategy covering prevention, release gates, and incident response. This pipeline includes static analysis via custom lint rules, multiple tiers of automated and manual testing, a pre-production early access build, staged rollouts, and feature flags with instant kill switches. As a result, critical defects are caught early in the development lifecycle before reaching the wider production user base.

    DEPTH ■■■■■16 min read5 days ago

    MobileReliability

    Sign in to save and rate

  5. Bringing post-quantum cryptography to geographically fenced key management

    Cloudflare introduced a post-quantum geographically restricted key manager in closed beta to enforce data sovereignty and protect customers against harvest-now-decrypt-later attacks. The team implemented a hybrid ML-KEM-768 and X25519 cryptographic design that separates globally distributed wrapped private keys from regionally restricted root keys. This ensures that decryption keys are only accessible within authorized geographical boundaries and fails closed if validation fails.

    DEPTH ■■■■■12 min read3 days ago

    Security

    Sign in to save and rate

  6. From 2,500 requests to 24: Rebuilding star history without the stargazers

    GitHub faced abuse and performance issues because tools were scraping user identities to reconstruct repository star history. The engineering team collaborated with maintainers to build a purpose-built aggregate endpoint that returns daily star counts without identities and filters by time before aggregation. This reduced request volume from thousands to a few dozen and eliminated heavy database scans.

    DEPTH ■■■■■8 min read12 days ago

    Microservices

    Sign in to save and rate

  7. I don't trust ON DELETE CASCADE

    Postgres ON DELETE CASCADE can cause production outages, replication failures, and performance degradation during large deletions or schema migrations due to long-running transactions holding locks and generating massive WAL. The author recommends using soft deletes with batched background cleanup instead to keep transactions short and bounded. This approach avoids table locks and simplifies data recovery.

    DEPTH ■■■■■5 min read5 days ago

    PostgreSQL

    Sign in to save and rate

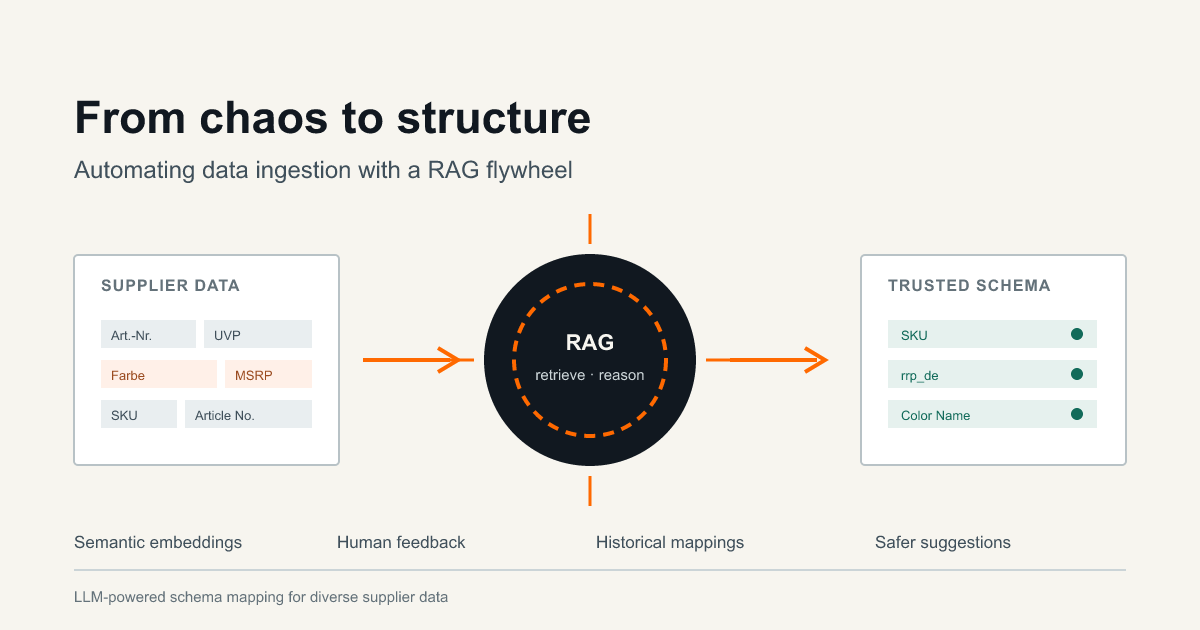
  8. Automating Data Ingestion with a RAG Flywheel

    Zalando replaced manual schema mapping for diverse supplier data with an LLM-powered Retrieval-Augmented Generation (RAG) flywheel. The system combines Amazon Titan embeddings stored in PostgreSQL via pgvector with tool-constrained generative models running at zero temperature. Every LLM suggestion passes through strict API validation checks before being reviewed by operations specialists, creating a continuous learning loop that improves future predictions.

    DEPTH ■■■■■14 min read2 weeks ago

    Machine LearningPostgreSQL

    Sign in to save and rate

  9. Thundering herd of circuit breakers

    An engineering team investigated why a client-side circuit breaker repeatedly failed to close on its own after an outage. By exporting OpenTelemetry traces into a custom visualization tool, they discovered that low probe traffic caused the autoscaler to scale down the service to minimum capacity, triggering a thundering herd of requests and immediate timeouts the moment the circuit breaker closed. Adjusting the system to account for capacity and probe representativeness prevents this oscillation.

    DEPTH ■■■■■10 min read2 weeks ago

    MicroservicesObservabilityReliability

    Sign in to save and rate

  10. Under the hood, off the hot path: How D1 scales to millions of databases

    Cloudflare scaled its serverless SQLite database, D1, to support millions of databases by decoupling the control plane from the data plane. The team used distributed metadata caching via Workers KV, optimized database connections through Hyperdrive, and implemented a self-correcting heartbeat mechanism. This architecture prevents centralized bottlenecks and allows D1 to handle rapid on-demand database creation efficiently.

    DEPTH ■■■■■22 min read13 days ago

    Databases

    Sign in to save and rate

  11. What gets TOASTed in Postgres

    This post examines how PostgreSQL uses TOAST to manage oversized rows and variable-length columns through compression and off-row storage. It compares the pglz and LZ4 compression algorithms across different workloads, highlighting trade-offs in search windows, file sizes, and CPU overhead. The analysis demonstrates how these mechanisms impact storage efficiency and read performance for large text and JSON data.

    DEPTH ■■■■■12 min read2 weeks ago

    PostgreSQL

    Sign in to save and rate

  12. “Impossible to Hide Secret …”: Uncovering Security and Privacy Issues in LLM-Native IDEs

    Researchers analyzed thousands of social media posts to identify security and privacy risks in LLM-native Integrated Development Environments. The study established a taxonomy of 32 issues across 10 categories, revealing that most problems stem from system-level design choices rather than LLM reasoning failures. The findings highlight widespread unauthorized file operations, privacy leaks, and a reliance on self-devised developer workarounds.

    DEPTH ■■■■■3 min read2 weeks ago

    Machine LearningSecurity

    Sign in to save and rate

  13. Improving site performance by shipping more CSS

    GitHub faced performance degradation on server-side rendering and initial page loads due to scaling issues with its CSS-in-JS solution. The engineering team executed a multi-year migration to CSS Modules and eliminated dynamic styling props using incremental rollouts, wrapper components, and automation tools. This resulted in significant performance gains, including 55% faster server-side rendering and the complete removal of styled-components.

    DEPTH ■■■■■8 min read4 weeks ago

    FrontendPerformance

    Sign in to save and rate

  14. Cloudflare deploys protections against php2shell vulnerability

    Recent disclosures revealed critical remote code execution and data exposure vulnerabilities in the PHP runtime. To mitigate the threat before public disclosure, Cloudflare developed full transaction detection to combine request and response signals within the WAF. This capability enabled automatic deployment of rules protecting customers against the php2shell exploits.

    DEPTH ■■■■■6 min read5 days ago

    Security

    Sign in to save and rate

  15. TIN v1.0.6: 2-3x faster, with support for stemming

    Following competitive benchmarks that highlighted opportunities for optimization, the developers of the TIN full-text search index for Postgres released versions 1.0.4 and 1.0.6. These updates added Snowball stemming for 18 languages, optimized top-k sorting queries with deterministic tiebreakers, and improved overall query performance. As a result, benchmark tests show that TIN outperforms competing extensions across conjunction, disjunction, and phrase query workloads.

    DEPTH ■■■■■8 min read2 weeks ago

    PostgreSQL

    Sign in to save and rate

  16. The Regression Tests Nobody Writes: Capturing How Software Actually Behaves

    Standard regression tests usually only verify developer intent rather than the actual, unwritten behaviors that systems accumulate in production over time. By capturing real production traffic and network-level interactions, teams can build characterization test suites to automatically detect unintended behavioral shifts. This approach prevents accidental regressions during legacy refactoring, rewrites, and major framework upgrades.

    DEPTH ■■■■■6 min read4 days ago

    Testing

    Sign in to save and rate

  17. 8 eMudhra certificates are compromised. Here's what you need to know

    Private keys associated with eight eMudhra intermediate certificates were compromised, allowing potential traffic interception. Cloudflare prioritized patching critical services, released client and tunnel updates, and deployed mitigations across its products. Customers are advised to upgrade affected software, update custom trust stores, and avoid disabling verification despite error messages.

    DEPTH ■■■■■4 min read5 days ago

    Security

    Sign in to save and rate

  18. Your next job doesn’t have a title yet: Emerging role skills Q&A with Cory Hymel of Andela

    Researchers analyzed thousands of job postings to understand how artificial intelligence is changing technical skill requirements. The findings indicate that instead of creating a workforce of pure generalists, the market is developing distinct new specialized skill bundles and hybrid roles. Consequently, organizations are facing talent debt as the half-life of technical skills rapidly shrinks.

    DEPTH ■■■■■15 min read12 days ago

    Testing

    Sign in to save and rate

  19. Smarter personalization: How property data helps us understand user price sensitivity

    Existing user personalization systems fail to systematically account for residential property values, leading to one-dimensional profiles and regional blind spots. A conceptual four-step method is proposed that combines public property data, large language models, building-level price estimation, and hierarchical clustering to classify user affluence. The approach remains unimplemented, with future viability depending on technical validation, data quality, and privacy approvals.

    DEPTH ■■■■■4 min read2 weeks ago

    Data EngineeringMachine Learning

    Sign in to save and rate

  20. Localizing compliance at scale: achieving South Korea’s ISMS certification

    To achieve South Korea's ISMS certification, Cloudflare had to modify its account sign-up flow to itemize required consents and disable third-party social logins that bypassed the form. By combining IP geolocation with user country selection, the team ensured localized compliance without breaking global functionality. The resulting certification provides a localized assurance benchmark for Korean users.

    DEPTH ■■■■■8 min read4 days ago

    Security

    Sign in to save and rate