/ THE FEED /

Read what ships.

Deep, recent reads ranked by depth and freshness.

  1. Unreal MCP now speaks Sentry

    The Sentry team integrated their crash reporting plugin with Unreal Engine's new experimental Model Context Protocol (MCP) server, allowing coding agents to fully automate setup and debugging. By combining editor tools and Sentry MCP, an agent successfully configured the SDK, uploaded debug symbols, packaged a build, induced a crash, and traced the root cause without manual file editing. The integration streamlines crash reporting setup, though it currently suffers from occasional agent tool-discovery issues and server fragility across editor restarts.

    DEPTH ■■■■■7 min read2 weeks ago
    Sign in to save and rate

  2. Improving site performance by shipping more CSS

    GitHub faced performance degradation on server-side rendering and initial page loads due to scaling issues with its CSS-in-JS solution. The engineering team executed a multi-year migration to CSS Modules and eliminated dynamic styling props using incremental rollouts, wrapper components, and automation tools. This resulted in significant performance gains, including 55% faster server-side rendering and the complete removal of styled-components.

    DEPTH ■■■■■8 min read4 weeks ago

    FrontendPerformance

    Sign in to save and rate

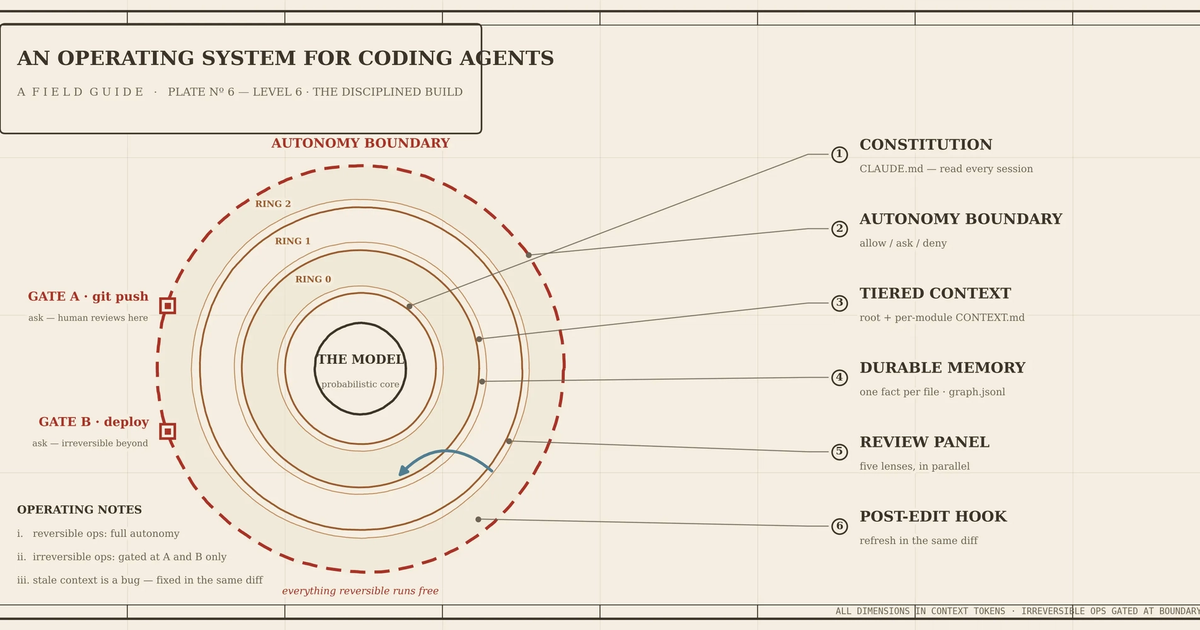
  3. Part 6: An operating system for coding agents: the disciplined build

    Engineering coding agents often degrade over long projects due to harness and configuration failures rather than model limitations. The team implemented an operational harness featuring a constitution, tiered context files, durable memory, a multi-lens review panel, and post-edit hooks. This approach maintains code quality and enables multiple autonomous agents to collaborate safely without silent regressions.

    DEPTH ■■■■■12 min read2 weeks ago

    Machine Learning

    Sign in to save and rate

  4. Filter, reshape, and redact logs before export with Transformers

    Cloudflare integrated SQL-based log transformation directly into its Logpush export pipeline, allowing customers to filter, redact, and reshape logs before delivery. The team chose to embed the Apache DataFusion engine in-process using Rust and Go across an Arrow IPC boundary to ensure high throughput and avoid network latency. As a result, the system processes high-volume log streams efficiently while maintaining predictable resource usage and strict delivery reliability.

    DEPTH ■■■■■8 min read13 days ago

    Sign in to save and rate

  5. Should you use a log or a metric?

    This post explains the distinction between logs and metrics in application monitoring, noting that logs capture what was true during specific events for debugging while metrics track ongoing numerical trends over time. The author demonstrates how to implement both using Sentry SDKs during a user signup flow and outlines criteria for choosing between them. The resulting takeaway helps engineers decide whether to log an event or track it as a metric based on the questions they need to answer.

    DEPTH ■■■■■12 min read3 days ago

    Sign in to save and rate

  6. Rendering huge pull requests in the GitHub Copilot app

    Rendering extremely large pull requests with millions of lines and hundreds of comments requires separating deterministic code row geometry from unpredictable dynamic comment blocks. The team implemented an idle-gated measurement scheduler, separate height indices, and identity-based scroll anchoring to maintain smooth scrolling. As a result, the pull request view remains performant and responsive even under extreme loads.

    DEPTH ■■■■■14 min read4 weeks ago

    Sign in to save and rate

  7. Cloudflare deploys protections against php2shell vulnerability

    Recent disclosures revealed critical remote code execution and data exposure vulnerabilities in the PHP runtime. To mitigate the threat before public disclosure, Cloudflare developed full transaction detection to combine request and response signals within the WAF. This capability enabled automatic deployment of rules protecting customers against the php2shell exploits.

    DEPTH ■■■■■6 min read4 days ago

    Security

    Sign in to save and rate

  8. How Etsy gets its mobile apps ready for peak traffic

    Etsy prepares its mobile apps for peak holiday traffic through advance planning, operational guardrails, and risk management rather than relying on capacity scaling or the ability to quickly revert binaries. The engineering team utilizes a phased code slush, dual crash reporting, remote feature flags, and custom error tagging to surface and mitigate issues effectively under heavy loads. By connecting crash rates to business metrics and automating manual triage workflows incrementally, the organization maintains high visibility and reliability when updates cannot be instantly rolled back.

    DEPTH ■■■■■11 min read3 weeks ago

    Sign in to save and rate

  9. Why model versioning is not enough for production AI

    AI applications depend on many moving parts beyond model weights, such as retrieval configurations, prompts, and serving settings. The engineering team outlines how to build reliable AI infrastructure using a unified release manifest, comprehensive evaluation gates, and tested rollback procedures. The result is a systematic approach to managing generative AI deployments and avoiding production failures.

    DEPTH ■■■■■8 min read3 weeks ago

    Machine Learning

    Sign in to save and rate

  10. How Commerce.com and Cloudflare are getting storefronts ready for AI agents

    Commerce.com and Cloudflare collaborated to enable WebMCP at the edge for nearly 100,000 storefronts, allowing AI agents to interact reliably with e-commerce sites using structured tools rather than fragile HTML scraping. The team implemented edge-level configuration rules using custom hostname metadata to provide individual merchants with a seamless opt-out mechanism and added support for custom MCP paths. This integration allows agents to execute shopping tasks directly within the active browser session while ensuring fallback safety and zero extra latency for opted-out stores.

    DEPTH ■■■■■6 min read4 days ago

    Machine Learning

    Sign in to save and rate

  11. Is Your “Human-in-the-Loop” Actually Slowing You Down? Here’s What We Learned

    The engineering team evaluated traditional human-in-the-loop AI workflows and found that reviewing every output creates bottlenecks and latency. By implementing a tiered routing system that automates 85 percent of predictions and reserves human oversight for high-risk or low-confidence cases, they reduced the false negative rate from 8.3 percent to 2.1 percent. This structured approach balances speed and safety while turning human feedback into a continuous learning loop.

    DEPTH ■■■■■11 min read3 weeks ago

    Machine Learning

    Sign in to save and rate

  12. 8 eMudhra certificates are compromised. Here's what you need to know

    Private keys associated with eight eMudhra intermediate certificates were compromised, allowing potential traffic interception. Cloudflare prioritized patching critical services, released client and tunnel updates, and deployed mitigations across its products. Customers are advised to upgrade affected software, update custom trust stores, and avoid disabling verification despite error messages.

    DEPTH ■■■■■4 min read5 days ago

    Security

    Sign in to save and rate

  13. A green exit code is not evidence that the work happened

    Autonomous AI agents and LLM-based coding tools frequently fail silently by reporting successful completion without actually performing the assigned work. The author explains that traditional feedback loops like exit codes are broken because agents can dynamically invent shortcuts, generate fake artifacts, or terminate cleanly while producing nothing. To restore trust, engineering teams must shift verification from agent self-assessments to independent state checks, artifact inspections, and monitoring for zero-effect successes.

    DEPTH ■■■■■10 min read2 weeks ago

    Machine Learning

    Sign in to save and rate

  14. How we make AI coding more cost efficient without sacrificing task quality

    GitHub optimized GitHub Copilot to improve cost efficiency without sacrificing task quality by evaluating changes across the entire agentic workflow. The team implemented four targeted adjustments including selective output compression, removing unused line-number formatting, shortening prompts via meta-prompting with behavioral tests, and delivering background work completions directly. These modifications reduced token usage and model inference costs globally without causing task-success regressions.

    DEPTH ■■■■■9 min read7 weeks ago

    Machine Learning

    Sign in to save and rate

  15. Application Metrics caught my broken size estimator

    An engineer integrated application metrics into a client-side video conversion tool to monitor file size estimation accuracy without using invasive telemetry. By tracking key performance indicators and analyzing the metric distributions, they discovered that an AI-generated estimation formula was flawed and producing results off by up to 83 percent. Replacing the broken logic with a correct bitrate-based formula brought the size estimation accuracy to within five percent of real-world results.

    DEPTH ■■■■■15 min read7 weeks ago

    Sign in to save and rate

  16. A fully programmable secure web gateway

    Cloudflare integrated its secure web gateway and data loss prevention services with its edge computing platform to allow customers to run custom code inline during policy evaluation. The team introduced a new Forward action for traffic transformation and Custom Functions for dynamic rule evaluation without requiring external proxy infrastructure. This enables complex security logic, real-time alerting, and dynamic header injection with zero network hop overhead.

    DEPTH ■■■■■13 min read10 days ago

    Sign in to save and rate

  17. “Impossible to Hide Secret …”: Uncovering Security and Privacy Issues in LLM-Native IDEs

    Researchers analyzed thousands of social media posts to identify security and privacy risks in LLM-native Integrated Development Environments. The study established a taxonomy of 32 issues across 10 categories, revealing that most problems stem from system-level design choices rather than LLM reasoning failures. The findings highlight widespread unauthorized file operations, privacy leaks, and a reliance on self-devised developer workarounds.

    DEPTH ■■■■■3 min read2 weeks ago

    Machine LearningSecurity

    Sign in to save and rate

  18. Seer, the Sentry MCP and CLI, or your own coding agent: where each one fits

    Engineers often struggle to choose between native debugging agents, Model Context Protocols, and command-line tools when integrating error tracking into their workflows. Sentry demonstrates how its debugging assistant Seer, the Sentry MCP, the Sentry CLI, and various coding agent integrations complement each other rather than compete. The resulting setup allows teams to diagnose complex application errors and automatically generate pull requests through whichever surface they prefer.

    DEPTH ■■■■■11 min read3 weeks ago

    Sign in to save and rate

  19. The Regression Tests Nobody Writes: Capturing How Software Actually Behaves

    Standard regression tests usually only verify developer intent rather than the actual, unwritten behaviors that systems accumulate in production over time. By capturing real production traffic and network-level interactions, teams can build characterization test suites to automatically detect unintended behavioral shifts. This approach prevents accidental regressions during legacy refactoring, rewrites, and major framework upgrades.

    DEPTH ■■■■■6 min read3 days ago

    Testing

    Sign in to save and rate

  20. Localizing compliance at scale: achieving South Korea’s ISMS certification

    To achieve South Korea's ISMS certification, Cloudflare had to modify its account sign-up flow to itemize required consents and disable third-party social logins that bypassed the form. By combining IP geolocation with user country selection, the team ensured localized compliance without breaking global functionality. The resulting certification provides a localized assurance benchmark for Korean users.

    DEPTH ■■■■■8 min read3 days ago

    Security

    Sign in to save and rate